

The last thing any security leader wants to wake up to is an early-morning alert about a breach. Yet, nearly 40% of IT security professionals believe their organization could face one within the next year.
For enterprises, balancing security, compliance, and customer experience is a significant challenge. Multi-factor authentication (MFA) has become a popular choice to mitigate risks, and while it is better than having no security measurements in place, there are multiple ways for hackers to take advantage of this method. Today, hackers are actively bypassing MFA through phishing, SIM swapping, and stolen credentials — gaining access, moving laterally, and escalating privileges quickly.
In fact, recent high-profile breaches have highlighted this weakness. In one incident, hackers bypassed MFA to gain unauthorized access to cloud service accounts and extracted credentials and session tokens in the process. In another, $1.3 billion was stolen in digital assets from a Dubai-based exchange.
These breaches showcase a crucial reality: authentication alone is no longer enough. To truly minimize risk, organizations must adopt dynamic, policy-driven authorization, such as attribute-based access control (ABAC), that evaluates context in real time. By enforcing granular, just-in-time access decisions, these authorization methods can reduce the blast radius of a breach and make it exponentially harder for attackers to move laterally.
Here’s how a robust authorization strategy can become a powerful deterrent to today’s most sophisticated cyber threats:
1. Stop privilege escalation with ABAC
When attackers get past MFA, they often seek privilege escalation. In traditional role-based access control (RBAC) environments, access is tied to static roles that often grant users more permissions than they actually need. This opens the gate for hackers. One stolen set of credentials can unlock far more than it should.
Excessive standing privileges are a major liability. Nearly 80% of high-profile system outages are linked to identity breaches involving over-permissioned accounts. The more standing access a user has, the greater the damage a compromised account can cause.
The solution? Remove unnecessary standing access altogether. With zero standing privilege (ZSP) or just-in-time (JIT) access, users get the access they need, only when they need it and nothing more. ABAC enables this precision by evaluating factors like device, location, and risk level in real time before granting access. That means even if a hacker gets valid credentials, they can’t just roam freely.
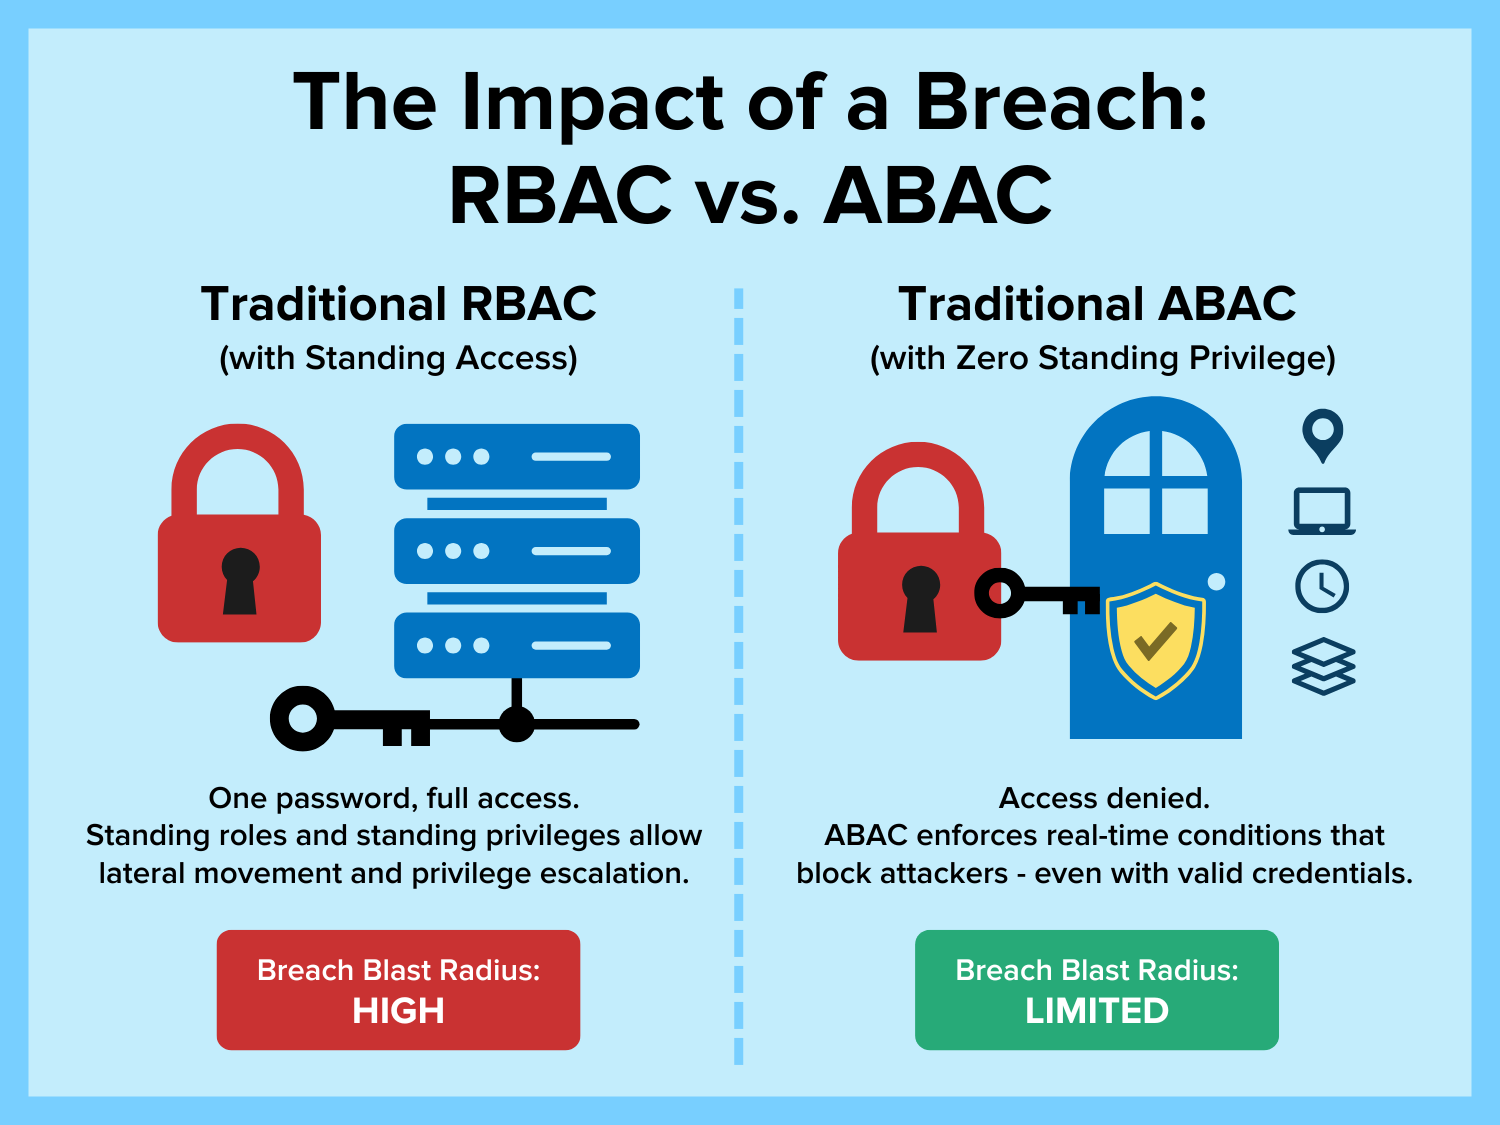
The need for the removal of standing access is especially showcased in the 2024 AT&T breach where an attacker accessed a dataset containing sensitive information on over 70 million people. The root cause? Overly permissive access controls and lack of segmentation. If standing access had been limited, and access dynamically enforced with ABAC, the attacker wouldn’t have been able to move as far, limiting the amount of money spent fixing the issue, customer dissatisfaction, and more.
2. Enabling Zero Trust
MFA only gets you partway. Without additional security, hackers will still find a way in, and when they do, they exploit the gaps left by legacy access models like RBAC. Once inside, bad actors move laterally — hopping from system to system using compromised credentials — often undetected.
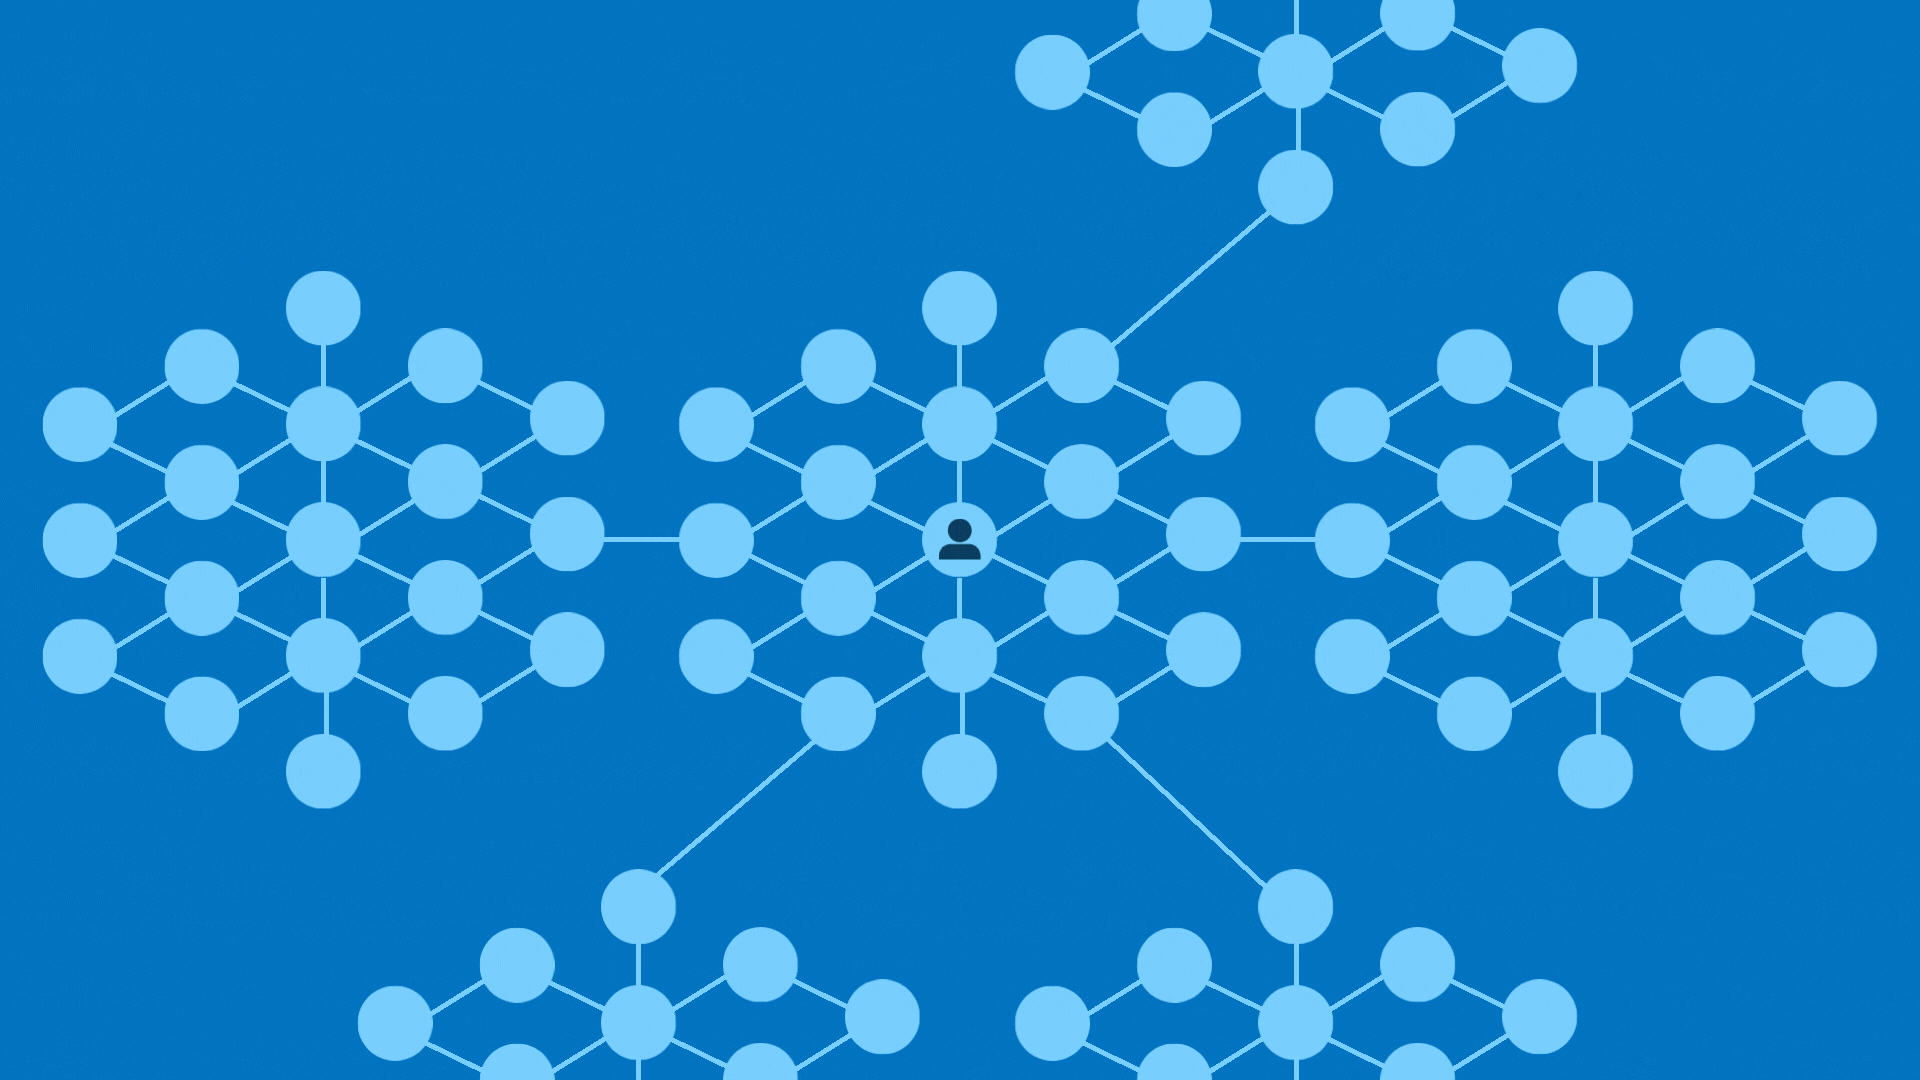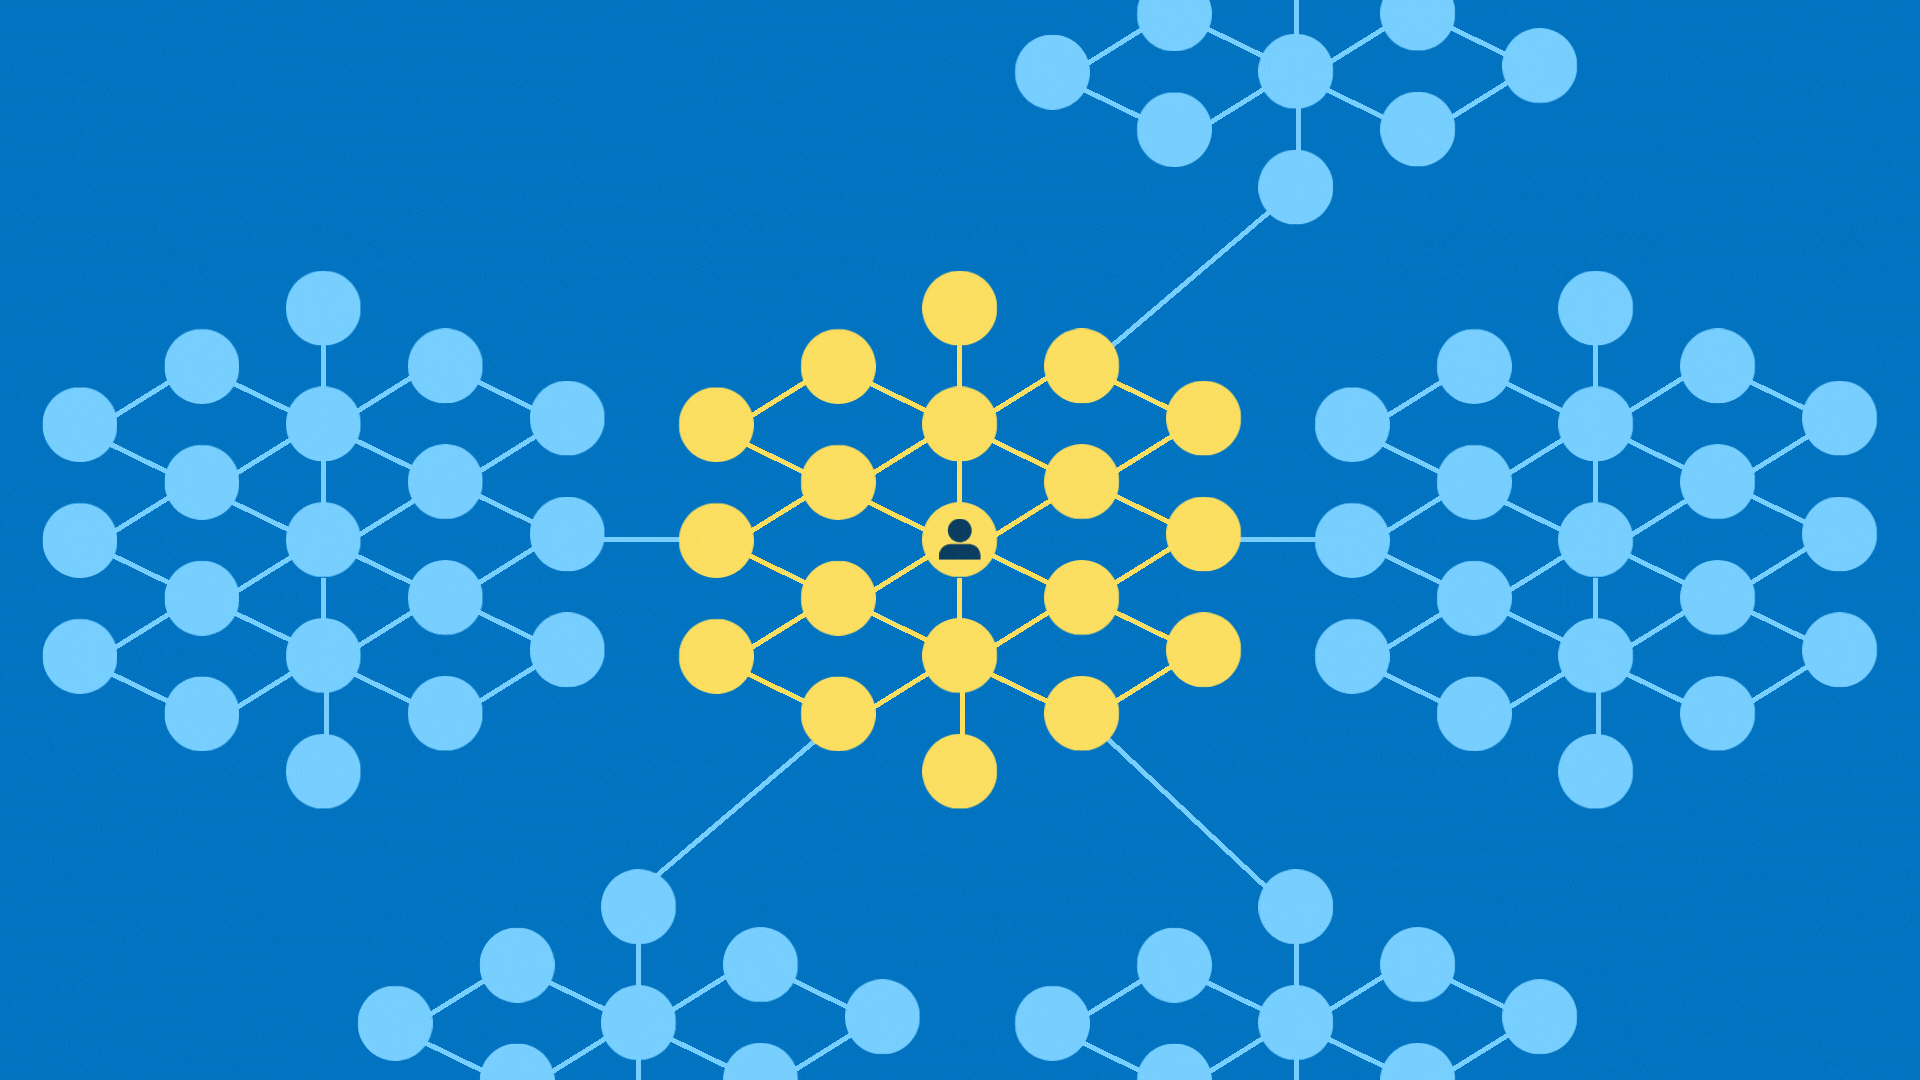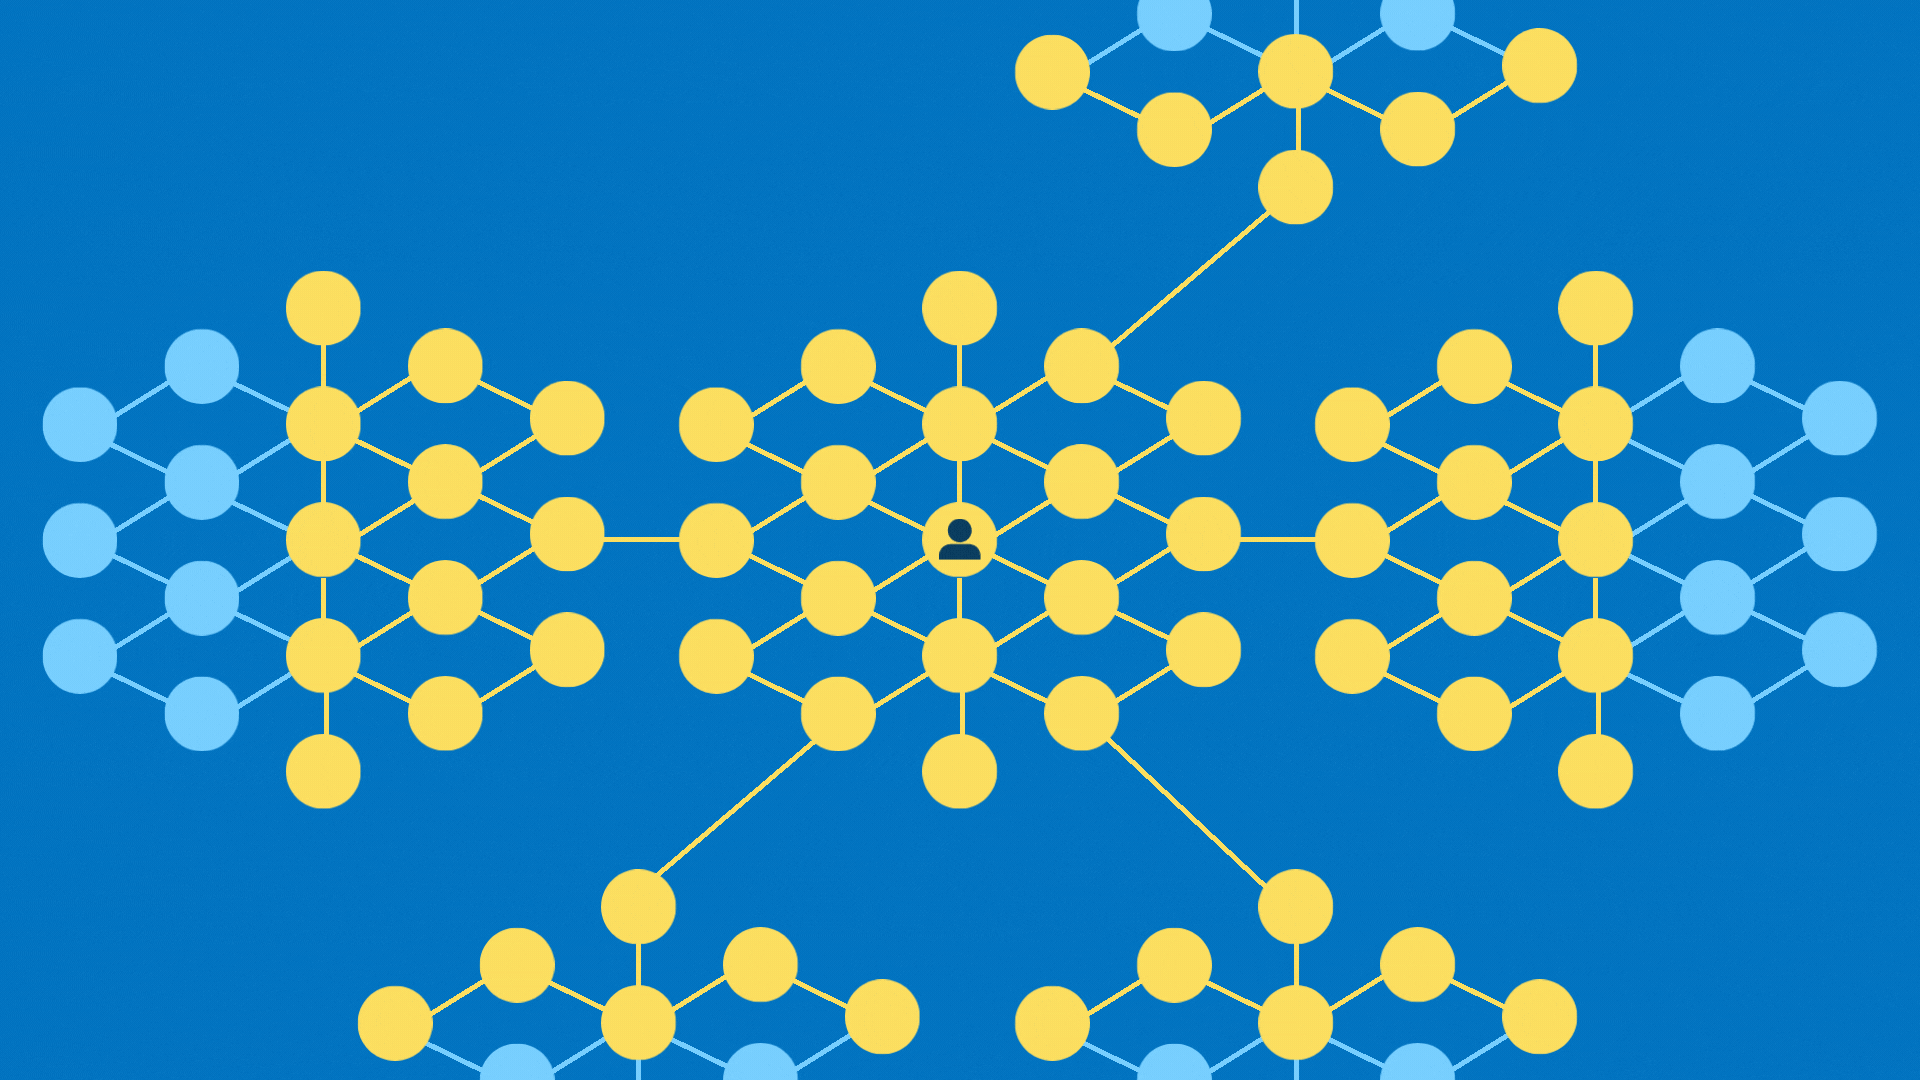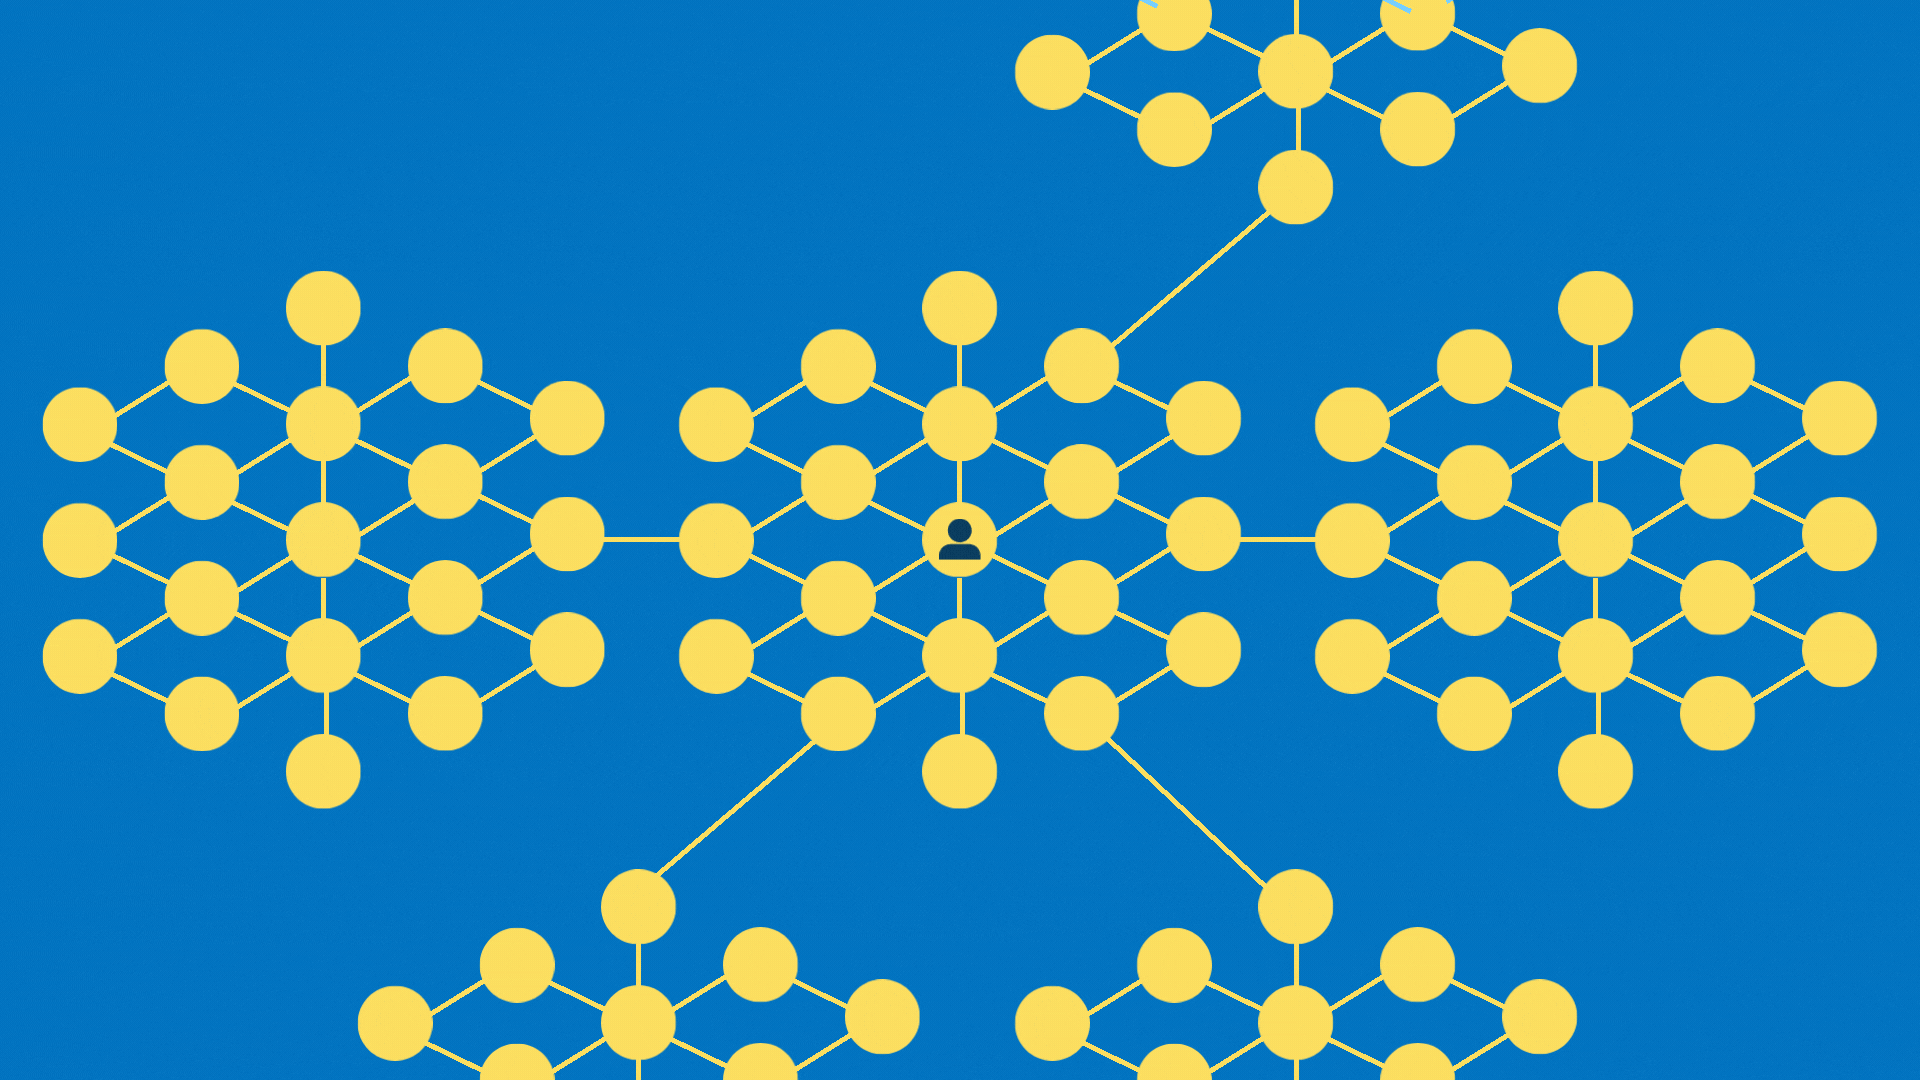
Standing access and excessive privileges enable hackers to move laterally
through roles associated with a compromised user identity.
With the help of ABAC, Zero Trust evaluates access in real time, based on a rich set of contextual attributes. This makes it so that even if an attacker has valid credentials, access isn't automatically granted; They must meet all defined policy conditions at that exact moment.

ABAC limits the blast radius of a breach by stopping lateral movement through policies that are set in place.
Consider the 2024 MITRE breach. Attackers exploited a zero-day vulnerability to compromise the VPN and take over an admin account. With ABAC or conditional access policies in place, that alone wouldn’t have been enough. Policies could have required access through a set of conditions such as a managed device, within a specific network segment, during business hours, or specific systems. Without meeting those conditions, access would be denied, effectively shutting down lateral movement and minimizing the blast radius.
3. Make access contextual to block threats
Modern attackers are relentless and fast. According to the latest Crowdstrike Global Threat Report, the amount of time for an adversary to start moving laterally across your network (also known as breakout time) has reached an all-time low. It now takes hackers only a matter of minutes to exploit overly broad roles, misconfigured permissions, and static policies to move in tandem and escalate privileges. What aids them? A lack of context.
MFA says who you are. ABAC decides what you’re allowed to do. Without that second layer, MFA is just a gate with no guardrails. As mentioned previously, ABAC adds real-time checks based on contextual signals so that even if they gain valid credentials or compromise a legitimate account, they’re faced with a wall of dynamic conditions they must meet, not just a static "yes or no" based on a role.
Today’s adversaries are using AI to rapidly test countless of these access combinations, relentlessly probing for vulnerabilities. If you’ve ever been a victim of identity theft, you know how quickly things spiral. Once attackers get a hold of your identity, they’re able to hit every credit card and online system before you even realize what’s happening. That’s the power of AI: speed and scale. Now, imagine that same approach applied to a corporate breach. It’s at a much larger scale. These attackers are often backed by well-funded, highly skilled teams and AI to orchestrate complex, coordinated attacks. In many cases, they’ve been preparing for this for months — or even years — waiting for the perfect moment to strike.
Context-aware authorization closes the gap. It shrinks the window of opportunity by continuously verifying that access aligns with expected behavior. For example, if there’s a login from a new location or an unusual device accessing sensitive data after hours, context-aware authorization will be able to permit or deny these requests based on a set of rules. Without the ability to meet precise access conditions, actors will struggle to pivot or escalate privileges.
On top of this, the stakes are higher than ever as there’s growing regulatory pressure from GDPR, HIPAA, PCI, and ITAR where fines can reach hundreds of millions. Fines, data loss, reputational damage, and stock drops often cost more than the breach itself. By adding context-aware authorization to your MFA, you can make sure your organization doesn’t pay the price.
4. Reduce insider threats
Insider threats are often the hardest to catch. Hackers frequently exploit compromised accounts, social engineering, weak MFA, or misuse of privileges to gain a foothold. Applying the principle of least privilege (PoLP) dynamically is essential, giving users the access they need only when they need it.
A high-profile example is the MGM Resorts breach, where attackers used social engineering to manipulate an insider and escalate privileges far beyond what was originally granted. Had ABAC been in place, the impact of the breach could have been limited even after privilege escalation as the attacker might not have met specific access conditions.
ABAC assumes threats can come from anywhere. By verifying each access request in real time, it reduces the risk of lateral movement and privilege escalation. While you can’t 100% eliminate the risk of a breach, policy-driven authorization narrows the attack surface.
5. Protect sensitive data with granular access controls
Even if attackers get in, ABAC ensures they won't have unrestricted access to sensitive information. With fine-grained, policy-driven controls, organizations can define exactly who can access specific information — when, how, and to what extent.
Features like data masking, encryption, and contextual restrictions ensure only authorized users can view or interact with sensitive data. Beyond strengthening security, these controls also support compliance with regulations like GDPR, HIPAA, and PCI DSS reducing the risk of exposure during both storage and transmission.
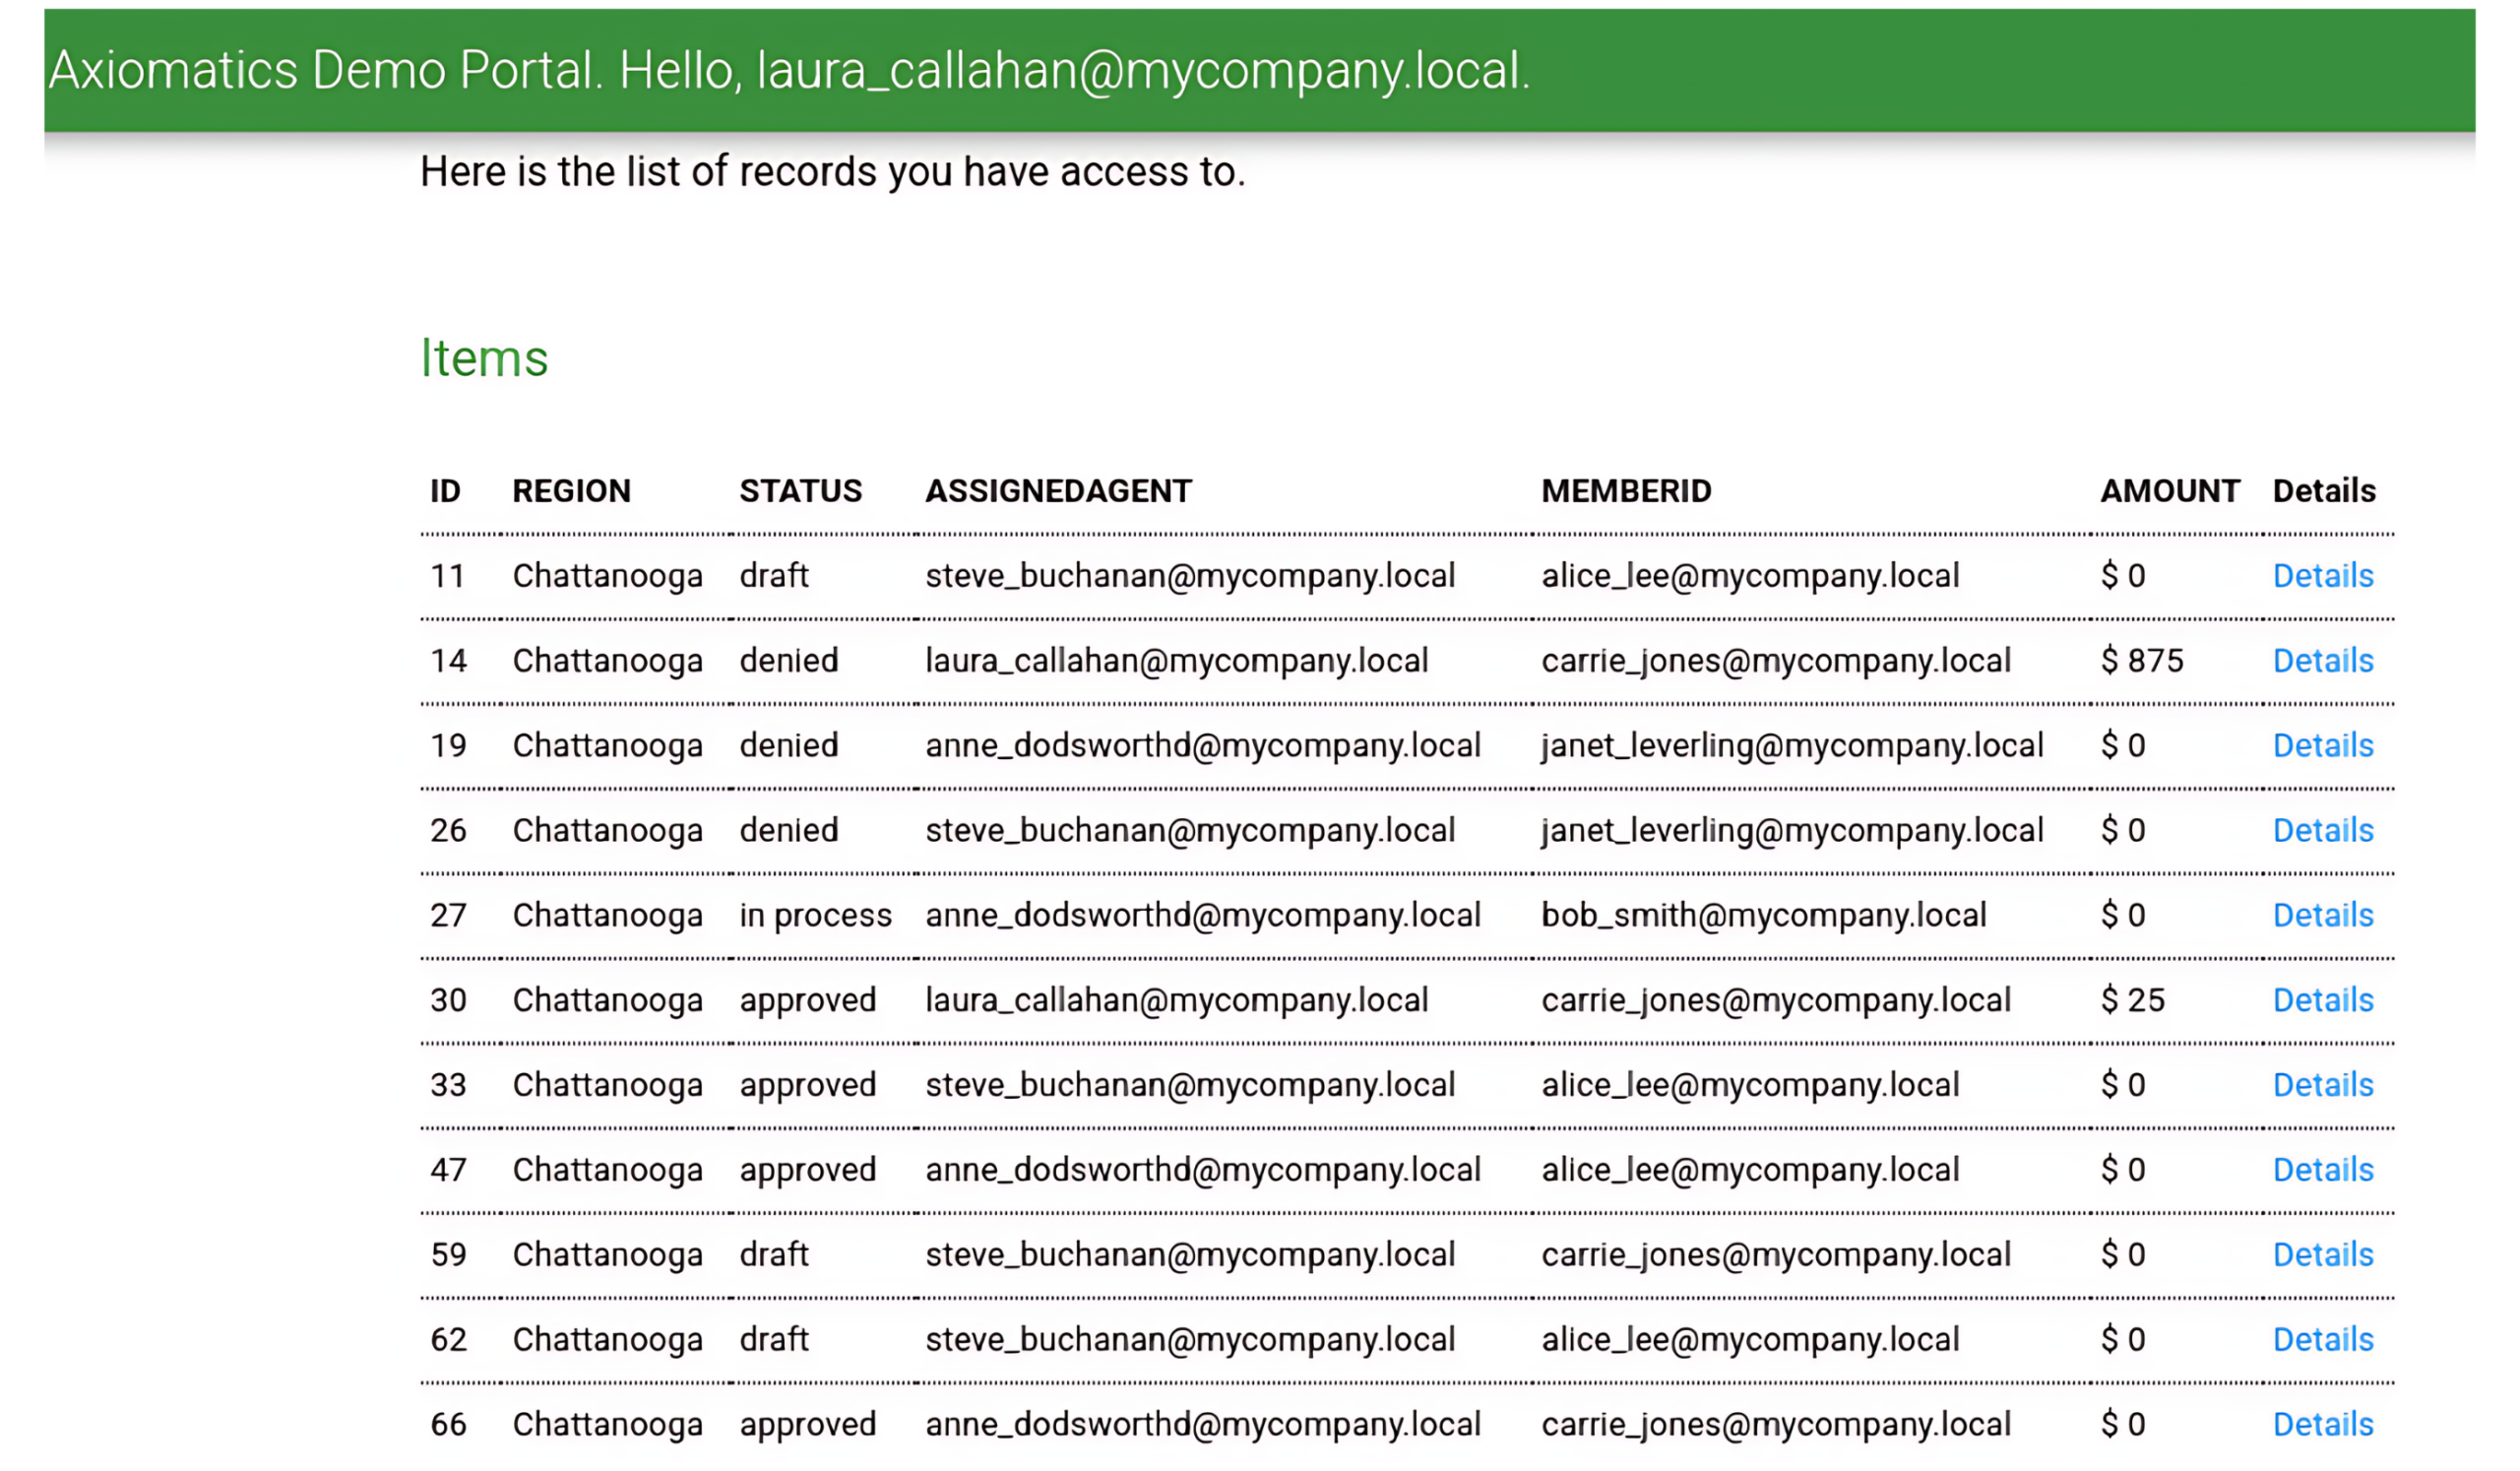
Limit the breach blast radius with ABAC
Hackers are actively targeting MFA and exploiting outdated access controls, but with dynamic ABAC, your organization doesn’t have to be next. By enforcing real-time, contextual policies, ABAC reduces the blast radius of a breach and limits what attackers can access.
Think of it as upgrading your data vault with motion sensors, biometric locks, and laser grids — instead of relying on a simple keycard.
If you want to learn more about how to effectively protect your business, we recommend reading the following guides:
- The State of Authorization: Playbook Edition
- Reaching Zero Trust with policy-driven authorization
- You’re either in or you’re out: The challenges of authentication
Want to see how we can help you secure your business? Sign up for a free demo with one of our solution experts.