1. Home
  2. |
  3. Protecting Microservices & APIs with ABAC, OAuth, and OpenID Connect

Protecting Microservices & APIs with ABAC, OAuth, and OpenID Connect

Microservices and APIs have become the foundation of modern applications, enabling organizations to deliver scalable, connected digital experiences. However, as services become more distributed, enforcing consistent access control across APIs and microservices becomes increasingly challenging.

What’s Inside

Securing APIs with Modern Authorization

We examine how organizations can strengthen API and microservice security by combining authentication, authorization, and open standards into a cohesive access control strategy.

By using policy-driven authorization, you can prevent:

  • Franken-scopes: Unintended combinations of scopes.
  • Scope explosion: Excessive scope creation to support growing use cases.
  • Embedded authorization logic: Access control scattered across microservices.

Take a Look Inside

Growing Need for API Protection

APIs are now the primary way users and services access sensitive data, making strong security essential. While API gateways provide baseline protection, they often lack the ability to enforce fine-grained, consistent access control across complex environments.

Without stronger authorization, organizations risk scope sprawl, over-permissioning, and embedded security logic. Policy-driven authorization helps enforce least privilege and improve visibility across modern API ecosystems.

A sneak peek at how you can protect microservices and APIS with dynamic authorization

API Gateway and Authorization Architecture Patterns

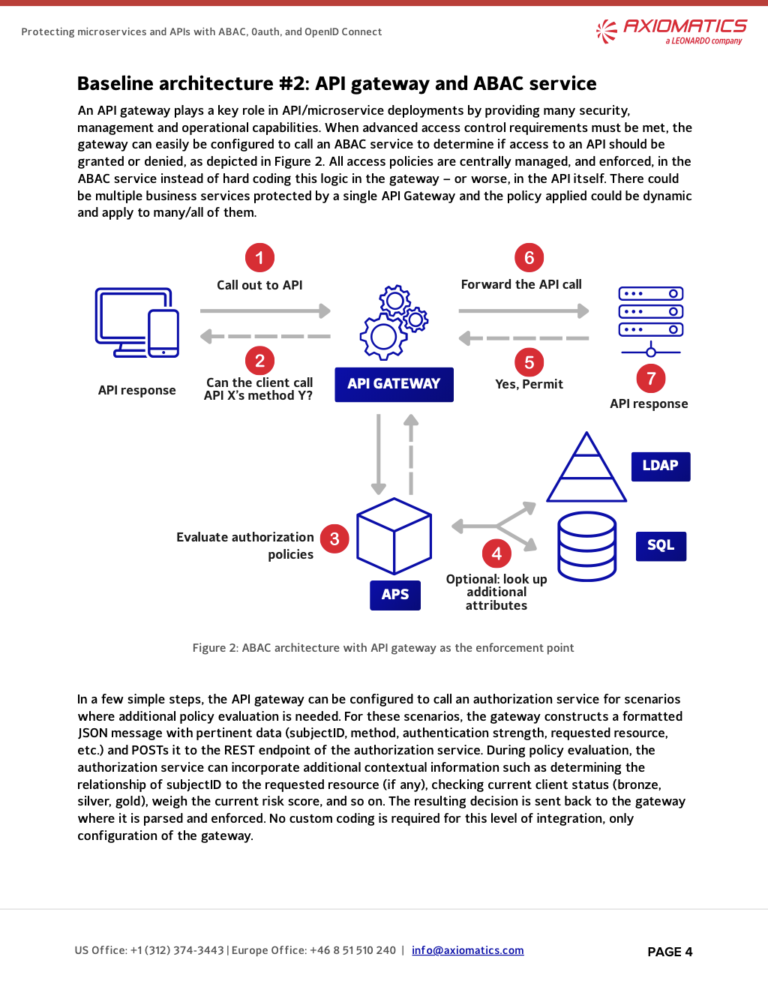
Modern API security typically combines an API gateway with standard authentication mechanisms to control access to backend services. This provides a baseline layer of protection for managing and validating requests.

For more advanced needs, the gateway can be extended with policy-driven authorization to enable centralized, context-aware access decisions. This approach allows organizations to enforce consistent, fine-grained control without embedding security logic directly into APIs or services.

Related Resources

AI
Company Updates

From AI to Authorization: Key Takeaways from Identiverse 2026

AI
Attribute-based Access Control

The Challenge Isn’t AI. The Challenge Is Authorization.

AI
Attribute-based Access Control

What Are MCP Apps and How Do You Secure Them? Using Dynamic Authorization for Enterprise AI Agents

Request a Demo

Take the Next Step in Securing Your Enterprise Systems

Schedule a meeting with our experts to discover how the Axiomatics Authorization Management Platform helps you implement fine-grained access control, support Zero Trust, and meet today's security and compliance requirements.

This website uses cookies

Cookies consist of small text files. They contain data that is stored on your device. To enable us to place certain types of cookies we need to obtain your consent. At , corp. ID no. , we use the following kinds of cookies. To read more about which cookies we use and storage times, click here to access our cookies policy.

Manage your cookie-settings

Necessary cookies

Check to consent to the use of Necessary cookies

Nödvändiga cookies

Cookie Syfte Lagringstid
consents

Används för att hantera samtycke

1 år
__hssrc

Närhelst HubSpot ändrar sessionscookien, ställs denna cookie också in för att avgöra om besökaren har startat om sin webbläsare.

Session

Functional cookies

Check to consent to the use of Functional cookies

Funktionella cookies

Cookie Syfte Lagringstid
messagesUtk

För att lagra webbläsarinformation och utförda åtgärder på webbplatsen.

6 månader

Cookies for statistics

Check to consent to the use of Cookies for statistics

Cookies för statistik

Cookie Syfte Lagringstid
__hssc

För att lagra anonymiserad statistik.

30 minuter
_gcl_au

För att lagra och spåra konverteringar.

3 månader


Personalization cookies

Check to consent to the use of Personalization cookies
In order to provide a better experiance we place cookies for your preferances

Cookies for ad-tracking

Check to consent to the use of Cookies for ad-tracking

Cookies för annonsmätning

Cookie Syfte Lagringstid
__hstc

För att lagra besökstid.

6 månader
hubspotutk

För att lagra och spåra en besökares identitet.

6 månader


Ad measurement user cookies

Check to consent to the use of Ad measurement user cookies
In order to show relevant ads we place cookies to tailor ads for you

Personalized ads cookies

Check to consent to the use of Personalized ads cookies
To show relevant and personal ads we place cookies to provide unique offers that are tailored to your user data