

Applications and Integrations
Secure your applications for everyday operations with scalable, dynamic authorization that adapts seamlessly - whether your systems are on-premises, in the cloud, or across hybrid environments.
Learn morePolicy-driven access decisions
powered by context
Axiomatics makes it easy to bring dynamic and fine-grained access control to any application.
Through connectors and policy enforcement points (PEPs), our solution integrates with countless systems, from enterprise to custom-built applications, enforcing consistent authorization everywhere.
Signals play a key role in a dynamic and fine-grained access control system. They can come from virtually any source, including identity providers, security solutions, or custom attributes unique to your organization.

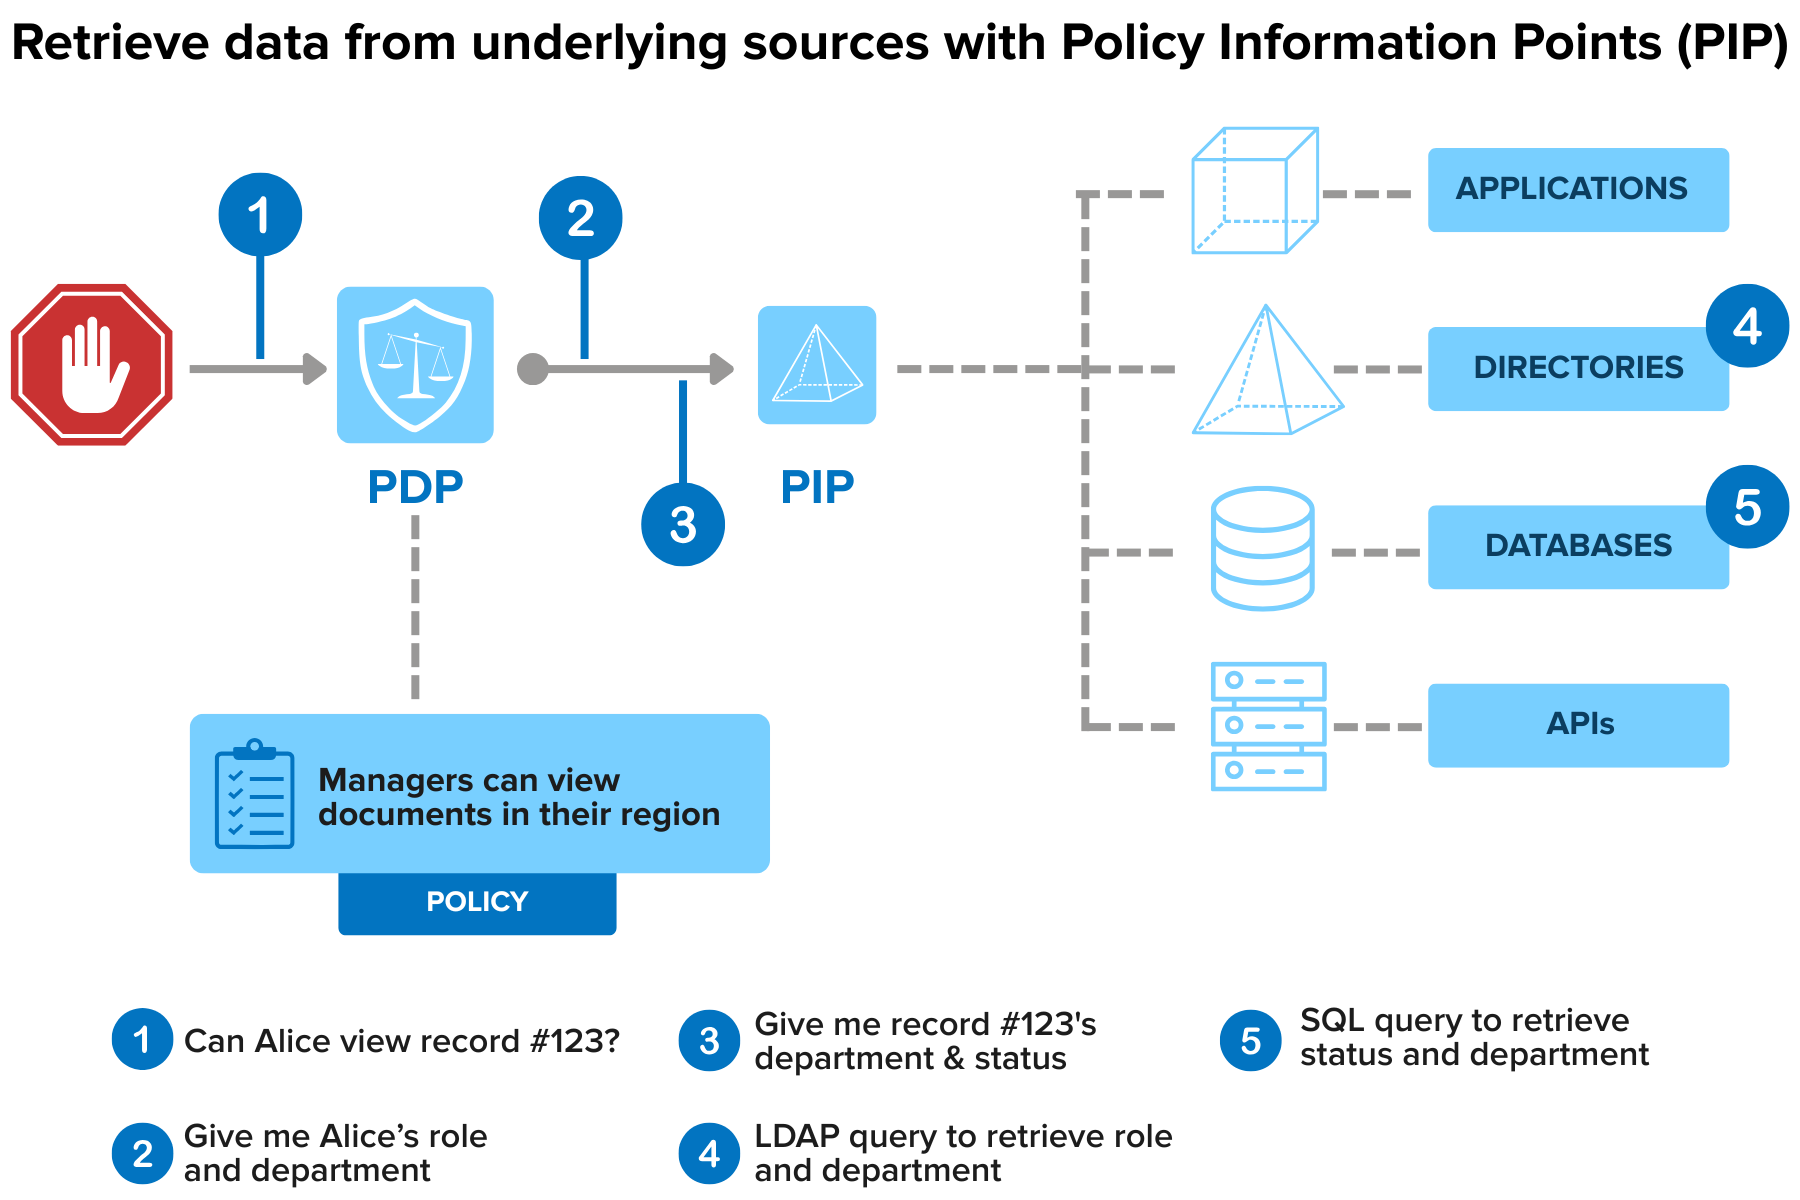
With policy-driven authorization, you can connect these signals to policies that determine contexts such as who is requesting access, what they are accessing, where and when the request occurs, and why access should be granted.
This approach shifts enterprises away from implied trust and towards a Zero Trust model.
Access decisions are continuously evaluated against real-time context, reducing risk while ensuring only the right people and machines can access sensitive resources.
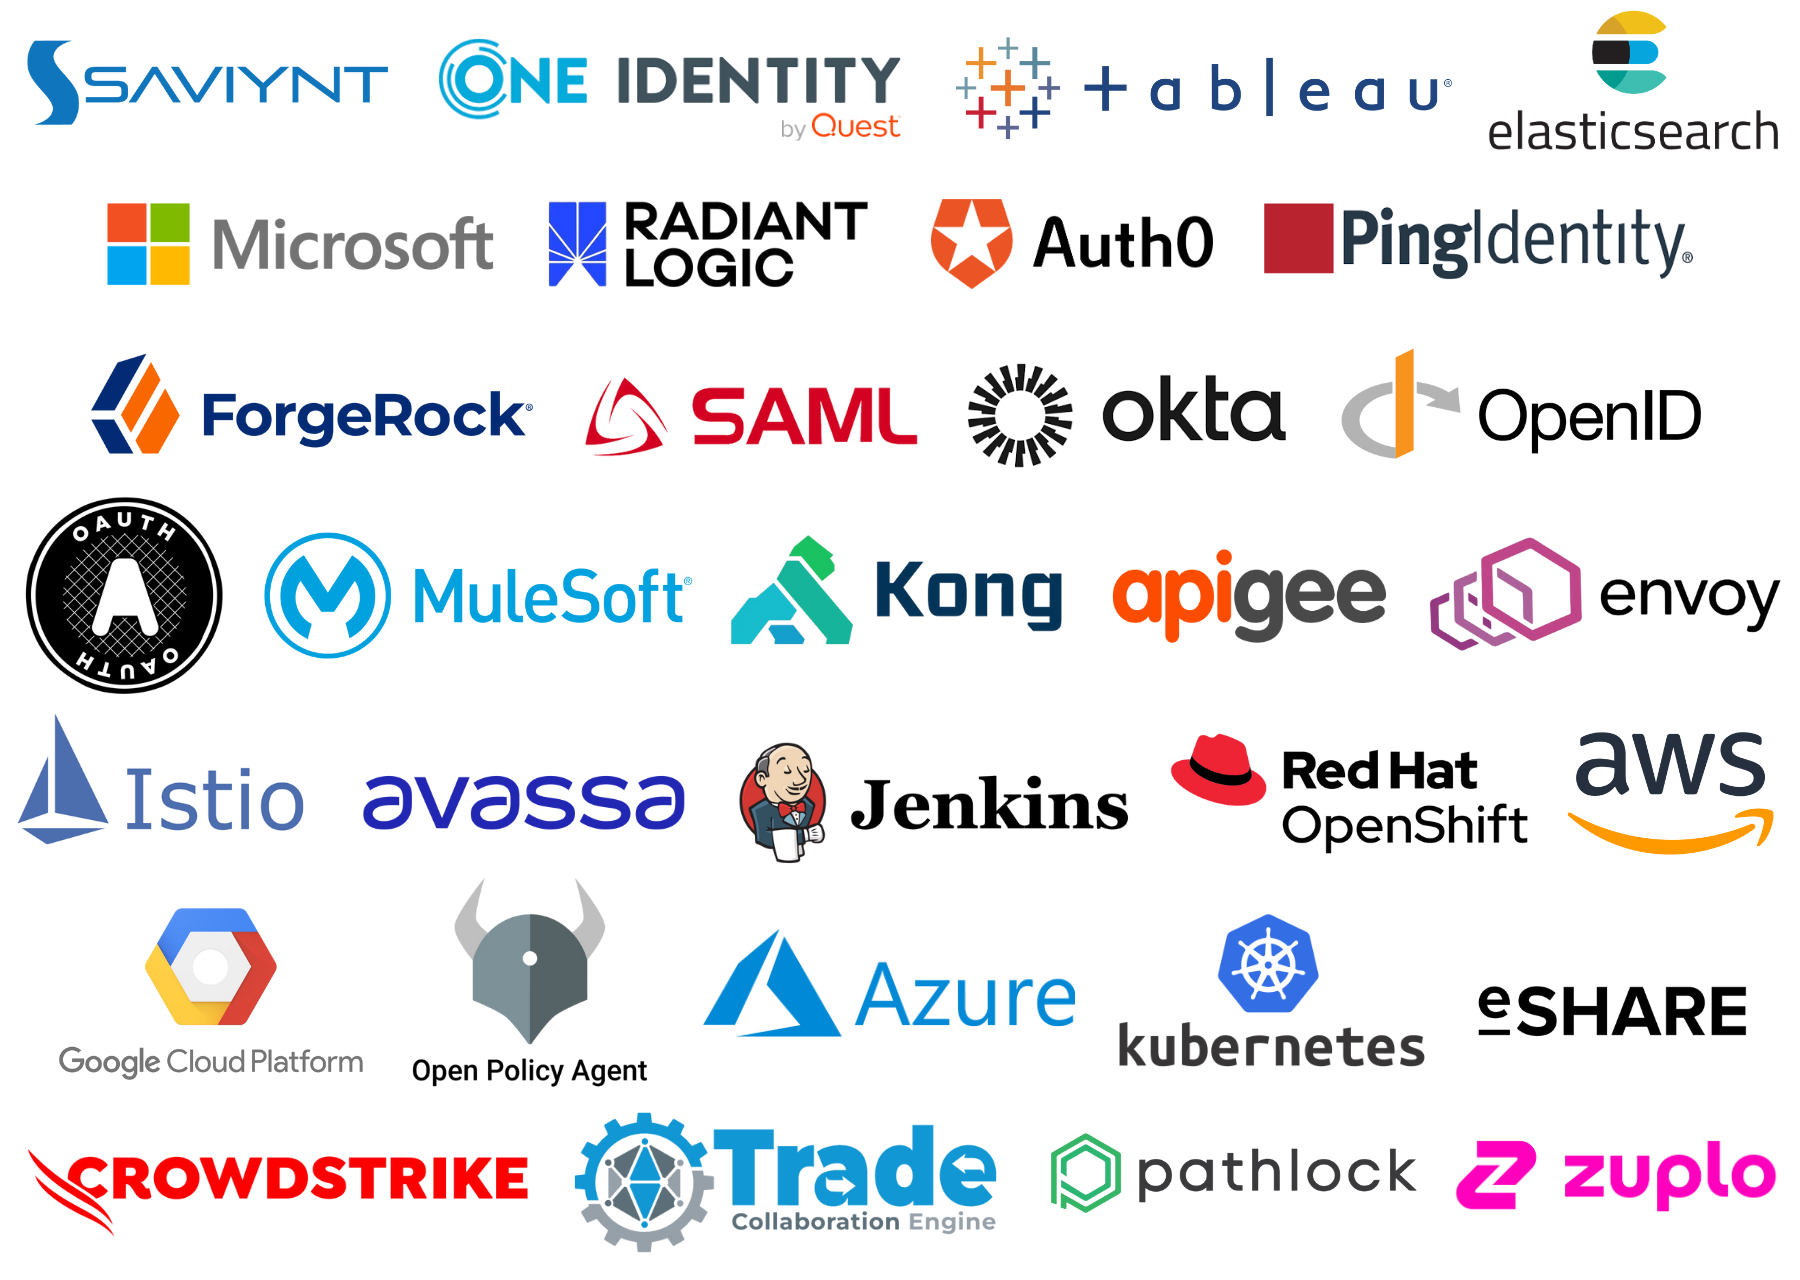
Meet some of our integration partners
Built on an API-first architecture and supported by out-of-the-box connectors,
Axiomatics integrates with a wide range of vendors and applications.
Our integration partners include:
Axiomatics delivers endless possibilities
to integrate authorization
Amongst the enterprise ecosystem, there are six common areas where Axiomatics will integrate:
Identity Providers
By being able to integrate with standards such as OAuth and OpenID, Axiomatics can connect to an enterprise’ existing authentication provider of choice, such as Okta, Ping, and Microsoft.
Cloud Platforms & DevOps
Axiomatics is often deployed in cloud-native environments and integrates with DevOps tools to support the creation, testing, and orchestration of authorization policies.
Microservices & APIs
Axiomatics can integrate its decision services with tools that support microservice and API infrastructures such as Envoy and Mulesoft.
Analytics
Enterprises often have many different types of solutions deployed for analytics. While Axiomatics can integrate its logs into any analytics solution, enterprises often choose to connect them with their Security Incident and Event Management (SIEM) solution.
Identity Governance
As organizations are seeking to move away from role-based access control postures, Axiomatics can integrate with an identity governance provider to include roles as one attribute in a dynamic authorization policy.
Identity Threat & Response
At the centre of a Zero Trust decision is a question of risk. With leading cyber security providers (such as TC Engine) providing real-time insights into user behavior, Axiomatics can leverage risk as a dynamic attribute to fulfill an identity threat detection and response outcome.
Flexible authorization for every application layer
Additionally, integration requirements will change from application to application. As a result, Axiomatics enables your organization to integrate into all layers of the application to serve the required run-time authorization outcome.
For example, if you want to enforce a dynamic policy at the microservice layer, Axiomatics provides multiple options to integrate directly with a microservice architecture.
Let's show you a demo and take the next leap in your authorization journey
Meet with us and see how our award-winning solution can help you meet today's application access control needs.
Request a demo