1. Home
  2. |
  3. Joiner, Mover, Leaver with Policy-driven Authorization

Joiner, Mover, Leaver with Authorization

Discover how policy-driven authorization helps organizations simplify employee access management, automate authorization decisions, and maintain least-privilege access throughout the entire JML lifecycle.

What’s Inside

Simplifying the Joiner, Mover, Leaver Lifecycle

Managing access shouldn't become more complicated every time an employee joins, changes roles, or leaves an organization.

We explore how policy-driven authorization helps organizations move beyond static roles and manual access updates by evaluating authorization requests in real time using current user attributes and contextual information.

Key topics include:

  • The challenges of traditional JML processes: How manual provisioning, static roles, and outdated permissions create security risks and administrative overhead.
  • Managing access throughout the employee lifecycle: How policy-driven authorization supports onboarding, internal mobility, and offboarding.
  • Preventing permission creep: How dynamic authorization helps ensure employees only access the resources required for their current responsibilities.
  • Automating authorization decisions: How attributes such as department, job title, employment status, and location help enforce least-privilege access.

Take a Look Inside

Access That Follows the Employee

IGA solutions excel at defining and certifying access, but they are not designed to make real-time authorization decisions. This creates a gap between what is approved and what is actually enforced at runtime, especially in fast-changing cloud and API-driven environments.

From their first day to their last, employees need access that reflects their current responsibilities. Policy-driven authorization helps organizations manage these changes without relying solely on manual role assignments and updates.

Joiners: Grant the Right Access from Day One

Help new employees become productive faster by evaluating access requests against their department, job title, employment status, and other relevant attributes.

Movers: Prevent Permission Creep

When employees change roles or departments, authorization decisions adapt to their updated attributes, helping prevent unnecessary access from accumulating over time.

Leavers: Reduce the Risk of Residual Access

When an employee's status changes to inactive, authorization policies can automatically deny subsequent access requests to protected resources, reducing reliance on manual permission updates.

By using current attributes to evaluate access requests, organizations can improve security, reduce administrative overhead, and maintain least-privilege access throughout the employee lifecycle.

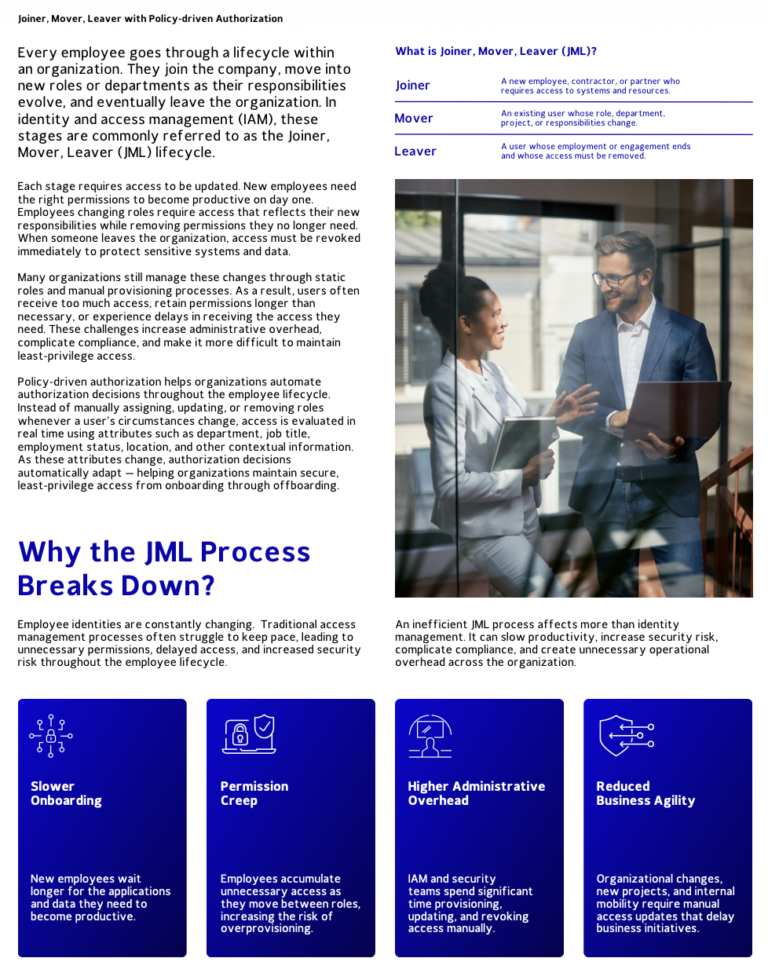
A look at the JML process and how policy-driven authorization helps

Related Resources

Request a Demo

Take the Next Step in Securing Your Enterprise Systems

Schedule a meeting with our experts to discover how the Axiomatics Authorization Management Platform helps you implement fine-grained access control, support Zero Trust, and meet today's security and compliance requirements.

This website uses cookies

Cookies consist of small text files. They contain data that is stored on your device. To enable us to place certain types of cookies we need to obtain your consent. At Axiomatics AB, corp. ID no. 556708-1012, we use the following kinds of cookies. To read more about which cookies we use and storage times, click here to access our cookies policy.

Manage your cookie-settings

Necessary cookies

Check to consent to the use of Necessary cookies

Nödvändiga cookies

Cookie Syfte Lagringstid
consents

Används för att hantera samtycke

1 år
__hssrc

Närhelst HubSpot ändrar sessionscookien, ställs denna cookie också in för att avgöra om besökaren har startat om sin webbläsare.

Session

Cookies for statistics

Check to consent to the use of Cookies for statistics

Cookies för statistik

Cookie Syfte Lagringstid
__hssc

För att lagra anonymiserad statistik.

30 minuter
_gcl_au

För att lagra och spåra konverteringar.

3 månader


Cookies for ad-tracking

Check to consent to the use of Cookies for ad-tracking

Cookies för annonsmätning

Cookie Syfte Lagringstid
__hstc

För att lagra besökstid.

6 månader
hubspotutk

För att lagra och spåra en besökares identitet.

6 månader


Ad measurement user cookies

Check to consent to the use of Ad measurement user cookies
In order to show relevant ads we place cookies to tailor ads for you

Personalized ads cookies

Check to consent to the use of Personalized ads cookies
To show relevant and personal ads we place cookies to provide unique offers that are tailored to your user data